Blog Menu G
Search
Categories
m
m

Category: Web Hosting

website optimization dashboard and growth 768x432

Friendly competition is fine in most instances, but there’s really no such thing if it’s competition in a business space. Especially if what’s at stake is your online business’ profitability versus having it going to your competitors. If you’re in eCommerce then you need to have your website serving as the primary engine for your success, and ideally your website is better than your competitors’ sites too. One area where it really ought to be better if your aim is to have maximum visibility for new customers is with its search engine optimization, or SEO as it usually is used as an acronym. And good SEO can definitely be included with website design. So yes your site can have good SEO right from the get-go, but what usually happens is that over time a site’s optimization needs to be revisited. Good SEO will by varying all the time based on the ever-changing algorithms of the search engines and that’s what it can be good to have a SEO audit for your site every several years or so. Often the folks you choose for website design in Toronto will be able to help you with that, or point your in the right direction to someone who really knows search engine optimization inside out. But it’s also something that you can get from you website hosting provider, and often for a much more agreeable price. That’s the case right here at 4GoodHosting, and over the course of 20+ years of being in this business we’ve definitely gained a rock solid understanding of what it takes to have a website reliably coming up on the first or second page of search engine results. That doesn’t apply to everyone here, but it certainly does for the SEO experts that we have on tap and ready to help eCommerce business owners with improving their site. There can be quite a spread of improvements that go into that, and it’s not just so simple as incorporating the right keywords at the right densities. If it were that simple then the fact that anyone and everyone can figure out how to use Google AdWords fairly quickly would...
You may find this interesting too.
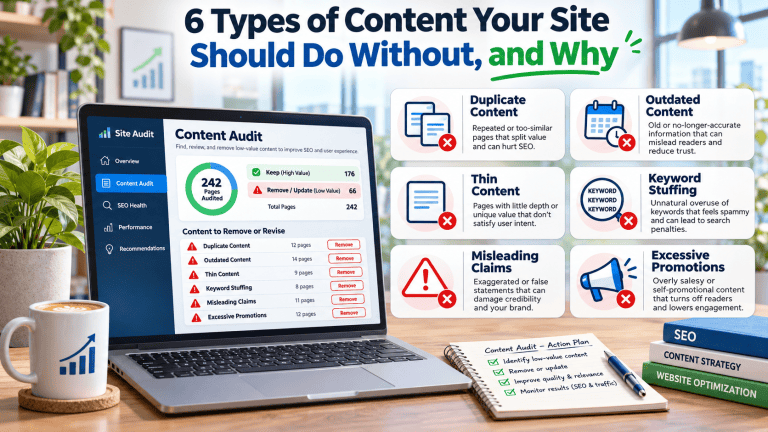
content audit six things to remove 768x432

More content isn't automatically a good thing. A site that publishes constantly but fills its pages with filler, duplication, or stale information is often worse off than one that publishes less but keeps every page genuinely useful — both for the people reading it and for how search engines evaluate it. The six categories below show up across sites of every size, usually added with good intentions, and each one quietly works against the site around it. 1. Thin Content That Doesn't Actually Answer Anything Thin content is a page that exists, technically answers a topic in its title, and says almost nothing once you read it: a few generic sentences, no real detail, nothing a reader couldn't have guessed before clicking. It shows up most often on pages created to fill out a template — a service page for every city a business claims to serve, a product description copied from a manufacturer's spec sheet with nothing added. Why it hurts: search engines don't index everything they crawl, and thin pages are one of the most common reasons they decline to. We cover exactly how that plays out — including the Search Console status that flags it — in why thin, duplicated pages quietly stop getting indexed. Beyond indexing, a reader who lands on a thin page and learns nothing leaves immediately, which is its own cost regardless of how the page ranks. What to do instead: write fewer pages and make each one genuinely answer the question it targets, with specific detail a reader couldn't get from a two-second glance. If a page can't say more than a sentence or two of substance, it usually shouldn't be its own page. 2. Duplicate or Near-Duplicate Content This takes a few common forms: the same paragraph pasted across a dozen location or service pages with only a city name swapped, a page copied wholesale from another site, or several pages on the same site quietly competing to answer the same question. Why it hurts: search engines index one version of duplicated content, not all of them, and when you haven't told them which version matters most, the one they pick...

You may find this interesting too.
canadian website modernization playbook 768x432

Most websites don't fail all at once. They erode. A plugin stops getting updated, a hero image balloons to four megabytes because nobody ever resized it, a contact form was wired up in 2019 and nobody has tested it since, and one day the site that used to load in two seconds is taking six. Nothing is technically “broken,” which is exactly why these problems survive so long — there's no error message forcing a decision, just a slow accumulation of friction that shows up in bounce rate, in support tickets, and eventually in rankings. A retrofit is the deliberate alternative to that slow decline, and to its opposite extreme: a full rebuild. Instead of tearing a site down and starting over, a retrofit treats the existing site as a structure worth keeping and upgrades it in place — the content, the backend, the hosting environment, the security posture — one load-bearing piece at a time. Done well, it's cheaper than a rebuild, faster to execute, and far less risky to search visibility, because the URLs, the internal link equity, and the content history that Google has already indexed stay intact. Done badly, a retrofit is just a rebuild with extra steps: changes made without a diagnostic baseline, a CMS migration rushed ahead of a security audit, a new theme installed on top of hosting infrastructure that was already the actual bottleneck. This guide lays out a sequenced, evidence-based approach to retrofitting a website — what to audit first, which fixes compound on each other, where the hosting layer does more work than people expect, and how Canadian businesses in particular should think about data residency and latency while they're at it. None of this requires a single enormous project with one launch date. The approach below breaks a retrofit into phases that can each be scoped, budgeted, and measured on their own, so a business can start with whichever phase is causing the most immediate pain — usually hosting and performance — and keep going as budget and priorities allow, rather than waiting for the ideal moment to fund the whole thing at once. What a Website Retrofit Actually...

You may find this interesting too.
4gh blog post pic.webp

Chrome ships browser updates constantly, and most of them never reach a business owner's radar — a new menu item, a redesigned settings page, a feature nobody outside Chromium's own team will notice. Every so often, though, an update changes something that actually touches how a website performs for mobile visitors, and two recent Chrome for Android changes fall squarely into that category. Neither one is a redesign or a new button. Both are changes to how the browser decides when to load content and how aggressively it tries to get ahead of what a visitor is about to do next — and both quietly shift more of the responsibility for a fast mobile experience onto the server the site is running on. That's the throughline worth paying attention to: as Chrome gets better at deciding what not to load yet and at guessing what to load early, the gap between a fast host and a slow one becomes more visible, not less. This isn't a full Core Web Vitals primer — that ground is covered elsewhere. This is specifically about these two updates, what they do, and what to actually check on the hosting side so a site benefits from them instead of getting caught out by them. Two Updates, One Pattern The first update, shipped in Chrome 148 (stable since early May 2026), adds native lazy-loading support for video and audio elements — the same deferred-loading behaviour Chrome has long supported for images, now extended to media. The second is the continued rollout of Speculation Rules–based prefetching and prerendering on Android, which lets Chrome request a page's content before a visitor has even tapped the link, based on signals that the tap is likely coming. Both features are, on paper, pure wins for the visitor: less data pulled down for content they haven't scrolled to yet, and pages that feel instant because they were already loading before the tap landed. The pattern underneath both of them is what matters for a site owner: Chrome is increasingly good at not asking for things until it needs them, and increasingly good at asking for things slightly before it needs them....

You may find this interesting too.
canadian domain extensions explained 768x432

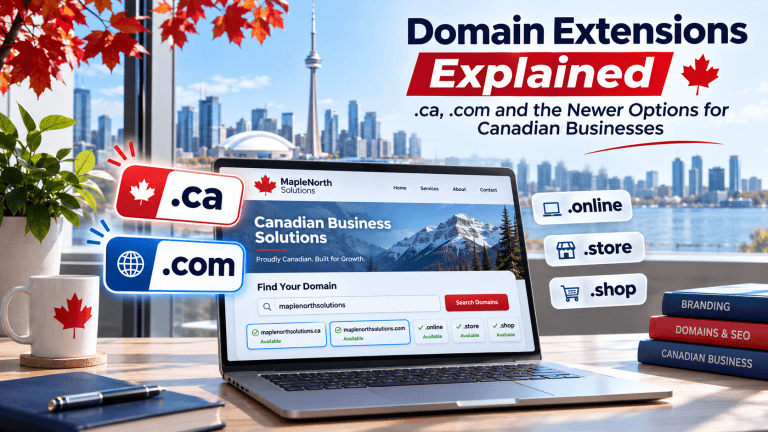
Choosing a domain name used to mean choosing between .com and, for Canadian businesses, .ca. Today there are hundreds of other endings available, from .shop and .tech to .online, .app and .law. Some are useful. Some are mostly marketing. A few carry risks that aren't obvious when you register them. The part of a domain after the final dot is called its extension, or top-level domain. It affects how customers read your address, how search engines interpret it, how email filters treat it, what it costs to renew, and in some cases how your website must be configured. It's worth understanding before you register one. A domain extension, or top-level domain (TLD), is the last part of a domain name, such as .ca, .com or .shop. There are three main kinds: country-code extensions like .ca, generic extensions like .com and .org, and newer generic extensions introduced since 2012 like .shop and .tech. For most Canadian businesses, .ca and .com remain the safest main choices, with newer extensions best used for specific campaigns or products. This guide explains the types of domain extensions, how the newer ones came about, how customers, search engines and email systems treat them, the costs and technical requirements to watch for, and when a newer extension makes sense for a Canadian business. The Main Types of Domain Extensions Every domain extension is managed by a registry, which sets the rules for who can register names and at what wholesale price. Registrars then sell those names to the public. The extensions fall into a few broad groups. Type Examples Who can register Notes Country-code (ccTLD) .ca, .uk, .de, .fr Usually limited to people or organizations connected to the country, depending on the registry Signals a national connection; .ca is managed by CIRA under Canadian presence rules Original generic (gTLD) .com, .net, .org Anyone .com is the default most people type; .org is common for non-profits but open to all Sponsored or restricted .gov, .edu, .int Restricted to specific types of organization Not available to ordinary businesses Newer generic (new gTLD) .shop, .tech, .online, .app, .law, .design Usually anyone; some have eligibility rules Introduced through ICANN's new gTLD...

You may find this interesting too.
4gh blog post pic.webp

A domain name is one of the few business decisions that's cheap to make and expensive to change. Registering one takes a few minutes. Changing it later means reprinting signs and vehicles, updating every listing and profile, moving email addresses, setting up redirects and accepting a dip in search visibility while everything settles. Small businesses that rush the choice often live with an awkward name for years because switching feels harder than putting up with it. For a Canadian small business, the decision has a few extra layers: whether to use .ca, .com or both, who is eligible for a .ca, how bilingual names work, and how to keep the domain legally and practically under your control. A good small-business domain name is short, easy to spell when heard aloud, clearly connected to your business name, free of trademark conflicts, and registered in your business's own name. For businesses serving Canadians, a .ca domain signals a Canadian presence, and registering the matching .com as well protects the name. This guide explains how Canadian domain names work, how to decide between .ca and .com, the principles behind a strong name, what actually matters for search, the legal checks to run first, and how to register, protect and connect your domain once you've chosen it. What Is a Canadian Domain Name? A Canadian domain name usually means a name ending in .ca, Canada's country-code top-level domain. Since 2000, .ca has been managed by the Canadian Internet Registration Authority (CIRA), a not-for-profit organization. CIRA doesn't sell domains directly to the public. You register a .ca through a CIRA-certified registrar, which is often a hosting or domain company, and the registrar submits the registration to CIRA on your behalf. Unlike .com, which anyone in the world can register, .ca has eligibility rules. CIRA's Canadian Presence Requirements limit .ca registrations to people and organizations with a real connection to Canada. Who can register a .ca The Canadian Presence Requirements cover a range of registrant types. For small businesses, the relevant ones are usually: Registrant type Typical small-business example Canadian citizen or permanent resident A sole proprietor registering in their own name Corporation incorporated under federal,...

You may find this interesting too.
No related posts found.
featured image 1200×628@1x 1 768x402

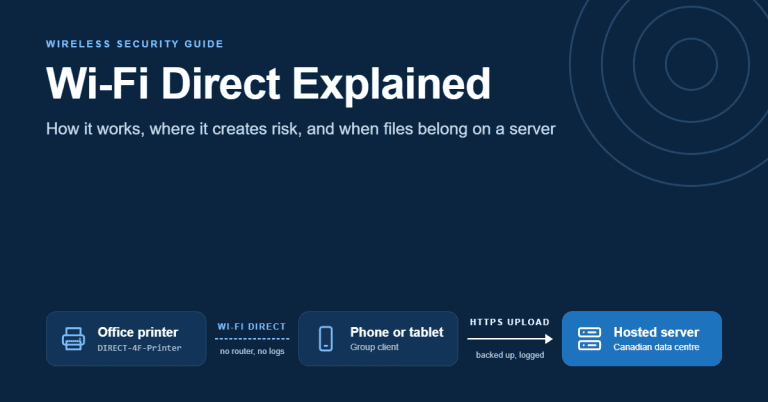
Open the Wi-Fi list on your phone in almost any office lobby and you will probably see a network nobody set up on purpose. It might be called DIRECT-4F-Printer-2ndFloor or DIRECT-xy-Boardroom. It doesn't appear on the network diagram and IT never configured it, yet it is broadcasting from a device a few metres from the accounting team. That network is Wi-Fi Direct at work. It's the reason a topic that sounds like gadget trivia belongs in a business conversation about infrastructure. Wi-Fi Direct is a Wi-Fi Alliance standard that lets two or more devices connect to each other over ordinary Wi-Fi radios without a router, access point or internet connection. One device takes on the job an access point would normally do. The others join it, and data moves directly between them at Wi-Fi speeds. The convenience is real. A guest can print from their phone, a laptop can mirror to a meeting-room display, and a large video can move between two phones in seconds. The same design also creates small, self-managed networks that sit outside the controls an organization relies on. They have no firewall policy, no central logging and no backup, and they pair using methods that were never built for hostile environments. This guide explains what Wi-Fi Direct is and how a connection actually forms. It compares Wi-Fi Direct with Bluetooth and newer peer-to-peer options, shows where it creates security exposure in an office, and sets out how to lock it down without breaking printing. It ends with the point where business files should stop moving device to device and start living on a properly hosted server. What Is Wi-Fi Direct? Wi-Fi Direct is a peer-to-peer mode of Wi-Fi. Standard Wi-Fi works like a hub with spokes: every laptop, phone and printer connects to an access point, and the access point moves traffic between them and out to the internet. Wi-Fi Direct removes the hub. Two devices that support it can find each other, agree on which one is in charge, set up an encrypted link and exchange data, with no router involved. The Wi-Fi Alliance, the industry body that certifies Wi-Fi products, launched its Wi-Fi Direct...

You may find this interesting too.
cyber ai speed surge 768x432

A few years ago, asking an AI model a question was slow and expensive enough that most businesses treated it as a novelty. That changed quickly. Stanford's 2025 AI Index estimated that the cost of running a model at roughly GPT-3.5-level performance fell from about US$20 per million tokens in November 2022 to about US$0.07 by October 2024, a drop of more than 280-fold in under two years. When something becomes that much cheaper and faster, it ends up everywhere, including on your website. Most commentary on faster AI focuses on the people using chat tools. Far less attention goes to the other end of the connection. Every AI answer that cites a page, every model refreshed with new training data, and every agent that checks a price or reads a returns policy on someone's behalf starts with a machine requesting a URL from a server. More and more often, that server is yours. The scale is no longer marginal. The 2026 edition of the Thales Imperva Bad Bot Report, covering full-year 2025, found that automated traffic made up about 53% of web traffic, up from 51% the year before, leaving human visitors at roughly 47%. Not all of that automation is AI, and not all of it is harmful. The direction, though, is unmistakable: a growing share of the requests your site answers come from software rather than people. That changes the question site owners should be asking. It used to be enough to ask whether a page loads quickly for a visitor in Halifax or Kelowna. Now the question is whether your hosting can absorb a steady background load of crawlers, fetchers and agents and still respond quickly to humans, to search engines, and to the AI systems deciding whether your content gets cited at all. This guide explains what has changed, what AI crawler traffic actually costs a website, how it connects to search visibility and indexing, and what to look for in a hosting environment that now has to serve both audiences. What is AI crawler traffic? AI crawler traffic is the portion of a website's requests that comes from automated systems collecting or retrieving content...

You may find this interesting too.
focused developer in a modern tech workspace 768x432

Anyone who makes all the effort required to write and assemble an online blog entry each week is going to believe that’s there’s considerable value in what they have to say. The subject matter will vary, but the majority of times if you build up an online readership and people start following your blog then you’re doing well with sharing good information via your content. There’s real value in having those followers building up too, and especially if you’re aiming to monetize your blog in the way so many bloggers are trying to do. You’ve got to have good quality content there consistently, and a lot of the time it will be best to be on affordable web hosting platforms. The best fit for affordability is usually going to be Linux shared hosting. At least for blogs that are created and maintained as part of a personal venture of any sort. For these folks their blogs are usually very simply laid out and it doesn’t require much in the way of available bandwidth for them to load quickly, and it’s not like there is ever going to be a surge of visitors looking to all ready the blog at the same time anyways. So the fact that it’s suitably reliable for their smaller website and the shared hosting is the least expensive options is going to be the foremost reason why most bloggers will go with this type of web hosting. The ultimate Linux hosting with cPanel is going to add to the appeal if they’re signed up with us here at 4GoodHosting. With cPanel controls it’s especially easy to be your own small-scale webmaster and make strategic reorientations with your blogger website to make it better. But we can imagine that most of these bloggers will be just fine with their basic site on a shared hosting server just as it is. Most websites are built with site architecture that fits best with Linux hosting and that means optimized performance, so it’s unlikely you’ll be doing much with the controls as it is. So what we’ll do with this week’s entry for OUR blog here is to look at...

You may find this interesting too.
canadian cloud security data center 768x432

Moving to the cloud did not remove security risk from the enterprise. It moved it. The physical data hall, the racks, the hypervisor and the network fabric became someone else's job, and in exchange your team inherited a new set of failure points: identities with too much reach, storage left open by a single misapplied policy, logs that were never switched on, and contracts that say less about security than anyone assumed. For Canadian organizations there is a second dimension most cloud security guides skip entirely. Where data sits, who controls the company that holds it, and which laws can reach it are not abstract questions here. Federal privacy law makes you accountable for personal information even after you hand it to a processor. Quebec requires an assessment before personal information leaves the province, and that includes moving it to a server in Ontario or British Columbia. Federal privacy reform is back before Parliament, and a new critical-infrastructure cyber law has been enacted. This guide covers both dimensions. It explains what enterprise cloud security actually involves, how the shared responsibility model divides the work, what cloud technology changes about defending an organization, and where the Canadian legal layer alters the design. It also covers a question vendor-written guides rarely ask: when part of an enterprise workload belongs on single-tenant infrastructure rather than shared public cloud. In short: Enterprise cloud security is the combination of identity controls, configuration management, encryption, monitoring, contracts and governance an organization uses to protect data and systems running on infrastructure it does not physically own. The provider secures the underlying platform; the customer secures what it builds, stores and grants access to on top of it. In Canada, that customer responsibility also includes knowing where personal information is processed and which jurisdictions can reach it. What enterprise cloud security covers Strip away the marketing and enterprise cloud security comes down to one practical question: for every system and dataset you run outside your own premises, who is responsible for each control, and can you prove that control is working? The word "enterprise" matters because scale changes the problem. A small business with one hosting account has...

You may find this interesting too.
chatgpt image sep 28 2026 07 04 31 pm 768x432

When people talk about ecommerce being transformed by web data, they usually picture competitor intelligence: scraping rival price lists, watching search rankings, counting social mentions. That work still has a place, and it is covered in our guide to collecting public web data responsibly. But it is not where the real change has happened for most online stores. The bigger shift is quieter. It concerns the data a store generates about its own visitors and customers, on its own website, every day. Orders, on-site search queries, abandoned checkouts, returns, support tickets and server logs make up the most accurate record a merchant will ever have of what its customers actually do. How that record is collected, where it is stored, who else can see it, and what the law says about it have all changed substantially in the last few years. This guide is written for Canadian store owners and the people who run their sites. It explains what first-party data is, why it now sits at the centre of ecommerce measurement, how collection works technically, and where your hosting quietly shapes both the quality of the data and your legal exposure. It also corrects two claims you will find in most articles on this subject: that a "cookieless future" arrived in Chrome, and that collecting more data is automatically better. General information, not legal advice. This article describes Canadian privacy and payment-security rules in general terms. It is not legal advice. Speak to a lawyer about your own obligations, particularly if you sell into Quebec or handle sensitive categories of personal information. What "web data" means for an online store now It helps to separate web data into four kinds, because they behave differently in law and in practice. First-party data is information your store collects directly from people interacting with it: page views, product views, search terms typed into your site search, cart contents, order history, account details, email engagement and support conversations. You collect it, you control it, and you are accountable for it. Zero-party data is a subset that customers volunteer deliberately, such as a size preference, a gift-reminder date or answers to a product-finder quiz....

You may find this interesting too.
chatgpt image sep 23 2026 11 43 21 pm 768x432

"Managed hosting" sounds like a simple product: you pay more, and someone else looks after your server. In practice it is one of the least consistently defined terms in the hosting industry. One provider's managed plan means it patches the operating system and nothing else. Another's means it updates your WordPress plugins, tests your backups and rescues you at 2 a.m. when a checkout breaks. Both use the same word. That is why most "pros and cons" lists are less useful than they look. They compare an idealised managed service with an idealised do-it-yourself server, and conclude that managed is easier but more expensive. That is true, and it does not help you decide. The better question is who does which job. Every website sits on a stack of layers: hardware, network, operating system, web server, PHP, database, control panel, application and content. Someone has to keep each layer secure, updated and working. Managed hosting moves some of those jobs to your provider. Which jobs move, and which stay with you, determines whether managed hosting is a bargain or an expensive misunderstanding. There is a timely example. PHP 8.2, still common on business websites, reaches the end of its security support on 31 December 2026, according to the PHP project. After that date it receives no further security fixes. On a fully managed plan, moving your site to a supported version is usually the provider's job, possibly with some testing on your side. On an unmanaged server, it is entirely yours, and if nobody does it, nobody does it. Multiply that by every component in the stack, and you have the real trade-off. This guide maps those responsibilities, then tests the pros and cons against them. It includes a cost comparison that counts your time, a Canadian angle most guides miss, and the questions to ask any provider before you sign. What "managed" actually means: a responsibility map The clearest way to understand managed hosting is to look at who is responsible for each layer under each type of hosting. The table below shows the typical pattern. Individual providers vary, which is exactly why you need to ask. Layer Shared...

You may find this interesting too.
chatgpt 43 768x432.webp

Every hosting company sells uptime, and almost every hosting company sells it with a number: 99.9%, 99.99%, occasionally five nines. The number is presented as the answer to a question, and it is worth being precise about what question it actually answers. It answers: how often did our server respond to a request? The question a business owner is actually asking is: how often was my website working? Those are not the same question, and the gap between them is where most real downtime lives. A WordPress site can return a clean HTTP 200 response with a white screen where the content should be. It can serve a homepage perfectly while the checkout throws a fatal error. It can load in two seconds for a visitor in Toronto and time out for a visitor in Halifax. It can look entirely healthy while the contact form has been silently failing to send for eleven days. Under every uptime SLA in the industry, all four of those sites were up. This article is about the difference. What actually takes WordPress sites offline — which is almost never a hardware failure — what a managed environment genuinely prevents, what it demonstrably cannot prevent no matter what the sales page says, and how to monitor your own site in a way that catches the failures the uptime number is blind to. It is written for Canadian business owners and the people who look after their sites: the ones who have been told managed WordPress hosting is more reliable, and want to know specifically what that buys and where the limits are. What an uptime SLA actually measures Start with the arithmetic, because most people have never done it. SLA figure Downtime allowed per month Per year 99.0% 7 hours 18 minutes 3 days 15 hours 99.5% 3 hours 39 minutes 1 day 19 hours 99.9% 43 minutes 8 hours 46 minutes 99.95% 21 minutes 54 seconds 4 hours 23 minutes 99.99% 4 minutes 19 seconds 52 minutes 36 seconds 99.999% 26 seconds 5 minutes 15 seconds Two things jump out. First, the difference between 99.9% and 99.99% is not a rounding detail — it...

You may find this interesting too.
4gh blog post pic.webp

Most advice on building a retail brand is about how things look and feel. Colour palette, typography, store layout, shelf presence, packaging, the tone of the signage, the workshop where everybody agrees on three adjectives. It is a large and well-developed body of work, and for a physical shop it is largely correct — when the customer is standing in your space, the space is the brand. Then the customer is not standing in your space. They are on a phone, on a bus, at 9:40 on a Tuesday night, with your site half-loaded and a payment method you do not accept. Nothing about your colour palette is relevant to what happens next. This article is about that second situation, which is now where most of a retail brand's damage occurs. Not because design does not matter — it does — but because design is the part everyone already works on, and the failures that actually destroy trust are almost entirely invisible to the business until a customer tells them, or does not. Written for Canadian retail businesses running a website alongside, or instead of, a physical location. It covers what breaks, in rough order of how badly it damages you, and what the infrastructure underneath has to do to stop it. What ‘brand’ becomes once the store is a website The useful starting point is to be precise about what transfers from physical retail and what does not, because a great deal of retail branding advice is written as though the online version is the same exercise on a smaller screen. It is not, for one structural reason. In a shop, staff absorb the failures. Online, nothing does When something goes wrong in a physical store — an item is out of stock, the card terminal is slow, the queue is long, the price on the shelf does not match the till — a person intervenes. They apologise, they check the back, they offer an alternative, they honour the shelf price. The failure still happened, but it was absorbed, and the customer's memory of it is mediated by someone who was visibly trying. Online there is no one on...

You may find this interesting too.
canadian cybersecurity data vault 768x432

Most server security guides are checklists, and checklists have a flaw that rarely gets mentioned. They record what you meant to do, not what is true on the machine today. A firewall rule added in March gets loosened during a late-night troubleshooting session in June and never tightened again. The automatic update job stops running after a package conflict, and nobody notices because nothing visibly breaks. A backup schedule runs faithfully for two years and has never once been restored. Every one of those servers would pass a checklist review. Every one of them is less secure than its owner believes. This guide asks a different question. Not "have you done the seven things?" but "could you prove, this afternoon, that each of them is still working?" That is what reliably secure means in practice: security you can verify on demand, rather than security you remember setting up. It's also the most useful answer to the question of how to secure a server for the long term. It's written for Canadian small and mid-sized businesses running websites, online stores, client portals and internal applications on rented infrastructure, whether that's a shared hosting account, a virtual private server or a dedicated machine. Each step covers what to do, why it matters, and the specific check that tells you it's working. It also covers two things generic guides tend to skip: who is actually responsible for each layer under different hosting arrangements, and what Canadian privacy law expects of you when something goes wrong. This piece stays at the level of the server itself. For the wider picture, including identity, third-party scripts and edge controls, see our guide to the broader security strategy for Canadian businesses. What a secure server actually is Any explanation of how to secure a server should start with what the goal looks like. A secure server is one where only the people and processes that need access have it, known weaknesses are closed within a defined time, data is protected in transit and at rest, abnormal activity gets noticed, and the business can return to a known-good state after a failure or compromise. Notice what that definition...

You may find this interesting too.
chatgpt image sep 7 2026 09 27 09 pm 768x432.webp

A plumbing website has one job, and it is narrower than most web design advice assumes. It is not to showcase your brand or to explain your history. It is to make the phone ring when someone with water on their floor searches for help, and to make you the obvious choice when someone with a planned renovation is comparing three companies. Those are two different visitors with two different urgencies, and a site that serves one badly serves both badly. The emergency caller needs your number and your service area in under five seconds on a phone, possibly at two in the morning, possibly on a weak connection in a basement. The planned-work customer needs evidence you are licensed, insured, competent and reachable, and will read considerably more before deciding. This guide covers all three parts of getting that right: the design decisions, the local search work, and the hosting underneath it. We are a Canadian web hosting provider, so the hosting section is the part we handle daily, and we have tried to be specific about which hosting factors genuinely matter for a trades business and which are marketing. It is written for the plumbing business owner who is either building a first website, replacing one that generates nothing, or trying to work out why competitors appear above them in local results. Where something requires a specialist, it says so rather than pretending otherwise. Start here: your two customers behave completely differently Almost every mistake in plumbing website design comes from designing for one visitor and forgetting the other. Getting this distinction clear first makes the rest of the decisions obvious. Emergency customer Planned-work customer Situation Burst pipe, blocked drain, no hot water, flooding Bathroom renovation, fixture replacement, new build, inspection Search behaviour “emergency plumber near me”, “plumber open now”, often on a phone “bathroom plumbing cost”, “plumber [city] reviews”, often on desktop, over days Time on site Seconds. They want a phone number Minutes across several visits. They are comparing What convinces them You answer, you cover their area, you can come now Licensing, insurance, reviews, photos of real work, clear pricing approach What loses them A...

You may find this interesting too.
4gh blog post pic.webp

SEO services are the work a specialist does to help your website earn more traffic, leads and sales from search engines. A complete engagement covers seven areas: an audit and strategy, technical fixes, on-page optimization, content, authority building, local search, and measurement. A good SEO agency in Canada adds a Canadian layer on top: French-language requirements in Quebec, anti-spam rules for email capture, privacy obligations for analytics, and Competition Bureau rules on reviews. This guide explains what each part of an SEO service should include, what it typically costs, the red flags that separate useful agencies from expensive ones, and how your web hosting fits into the picture. Key takeaways A credible SEO proposal lists specific deliverables, names what is not included, and explains how success will be measured in leads or revenue, not just rankings. No one can guarantee a first-place ranking on Google. Treat any guarantee as a warning sign. Survey data puts the average SEO retainer at about US$2,900 a month, with local SEO averaging about US$1,560. Most providers charge a monthly retainer. AI summaries in Google now reduce clicks on many searches, so good agencies measure leads and calls, not traffic alone. Server location is not used by Google for geotargeting. Hosting affects SEO through speed, uptime and reliability. What Do SEO Services Actually Include? SEO services are a bundle of related work, and agencies package them differently. Before comparing proposals, it helps to know the full menu and what "good" looks like for each item. Component What you should receive Red flag Audit and strategy A written audit of technical, content and competitive issues, ranked by impact, plus a plan with priorities and timelines A generic automated report with no prioritization Technical SEO Fixes for crawling, indexing, site speed, mobile usability, redirects and structured data "Technical SEO" that never produces a list of changes On-page optimization Rewritten titles, headings and page copy matched to search intent, with internal linking Keyword lists pasted into existing pages Content New and refreshed pages that answer real customer questions, with briefs you can review A fixed quota of short blog posts with no strategy behind them Authority building Earned...

You may find this interesting too.
4gh blog post pic.webp

Elasticsearch is a fast, capable search engine, and it powers product search, site search and log analysis for thousands of businesses. It also has one of the worst track records in the industry for accidental data exposure, because a misconfigured server will hand its entire contents to anyone who finds it. The software is not the villain. The risk comes from how easily it is deployed, how much it needs to run well, and how rarely the people running it treat it like the database it effectively becomes. This guide covers nine reasons to be cautious, a hardening checklist, what Canadian privacy law expects if something goes wrong, and why the Canadian data center your index sits in matters as much as the configuration file. Key takeaways Most Elasticsearch data leaks were not hacks. They were servers left reachable from the internet with no password. Elasticsearch 8.0 and later turn security on by default, so today's risk sits mainly with older versions and with clusters where someone switched security off. Elasticsearch is a search index, not a system of record. Keep the authoritative copy of your data in a proper database. It needs generous memory and steady maintenance. An undersized virtual server is a common source of outages. Under PIPEDA, an exposed index holding personal information triggers a breach assessment and a record you must keep for 24 months, even if you cannot prove anyone accessed it. What Is Elasticsearch, and Why Do So Many Businesses End Up Running It? Elasticsearch is an open-source search and analytics engine built on the Apache Lucene library. It stores data as JSON documents, indexes every field, and returns full-text search results in milliseconds, even across millions of records. Applications talk to it through a REST API over HTTP, by default on port 9200. Many businesses run Elasticsearch without ever deciding to. It arrives as a dependency: E-commerce platforms. Magento Open Source and Adobe Commerce made a dedicated search engine mandatory from version 2.4, so every store on a current version runs Elasticsearch or a compatible engine. WordPress and other CMS plugins. Search plugins for larger content sites offload queries to an Elasticsearch server...

You may find this interesting too.
chatgpt image sep 4 2026 09 36 13 pm 768x432.webp

Canadian VPS hosting occupies an awkward middle ground. It costs several times what shared hosting does, it asks more of you technically, and the sales pages describing it are written almost entirely in specifications that mean nothing until you know which of them constrains your site. So this guide is organised around the decision rather than the product. The first question is whether you need a VPS at all, because a large share of businesses who buy one did not need to and a smaller share needed one two years before they bought. The second is managed or unmanaged, which is the choice people most often get wrong and the one with the largest hidden cost. Only then do specifications matter. It also covers what a VPS genuinely fixes and what it cannot touch, since the most common disappointment with a VPS upgrade is a site that is still slow afterwards. That outcome is predictable in advance, and predicting it correctly saves the money. The Canadian dimension is real but narrower than most hosting marketing suggests: latency for Canadian visitors and data residency are genuine considerations, and a Canadian IP address is not a search ranking advantage. Both are covered honestly below. What a VPS actually is A virtual private server is a partition of a physical machine with resources allocated to you specifically. You get a defined amount of CPU, memory and storage, your own operating system instance, and root or administrative access. Other customers share the same hardware, but not your allocation. That last distinction is the whole product. On shared hosting, your site's performance depends partly on what other accounts on the machine are doing, because CPU and memory are pooled. On a VPS, your allocation is yours whether the neighbours are busy or idle. You are buying predictability rather than raw speed. Type Resource model What you manage Typical fit Shared Pooled across many accounts Nothing below the control panel Brochure sites, low-traffic blogs, early-stage businesses VPS Allocated to you, on shared hardware Depends on managed or unmanaged Growing sites, ecommerce, uneven traffic, custom software needs Dedicated An entire physical machine Full stack, or the provider's...

You may find this interesting too.
chatgpt 30 768x432.webp

Most guides to Google mobile-first indexing are written as though it were coming. They tell you to prepare, to audit, to make the transition. That framing is several years out of date: Google announced the completion of the mobile-first indexing migration in October 2023, in a Search Central post titled “Mobile-first indexing has landed”. There is nothing left to prepare for. Google crawls and indexes the web with its smartphone crawler, and the mobile version of your pages is the version that determines what gets indexed and how it ranks. That is simply the current state of Search, not an upcoming change. Which changes the useful question. It is no longer “is my site mobile-friendly?”, and Google reinforced that by retiring the tool that answered it. It is now something more specific and more consequential: does the mobile version of your page contain everything Google needs to index, and can a person on a mid-range phone on mobile data actually use it? Those are different questions with different answers, and most sites that pass the first fail the second. This guide covers what mobile-first indexing actually means, the widely repeated misconceptions about it, the tools Google has retired and what to use instead, and the failure mode that causes real ranking damage. Mobile SEO in 2026 is largely about content parity, and almost nothing about a binary friendliness verdict. What mobile-first indexing actually means Mobile-first indexing means Google uses the mobile version of your content for indexing and ranking. Googlebot crawls as a smartphone user agent, renders the page as a mobile browser would, and indexes what it finds there. The single practical consequence, from which nearly everything else follows: if content exists on your desktop layout but not on your mobile layout, Google may not see it at all. Not rank it lower. Not see it. A page whose mobile version hides half its content is, from Google's perspective, a page with half that content. Three misconceptions worth clearing up “There is a separate mobile index.” There is not. There is one index, built from the mobile version of pages. Your desktop rankings are determined by what Google found...

You may find this interesting too.
On This Page G
Explore 4GOODHOSTING
Copyright © 2026 4GoodHosting. All Rights Reserved.
.CA by CIRA
+1 866 708 4678