



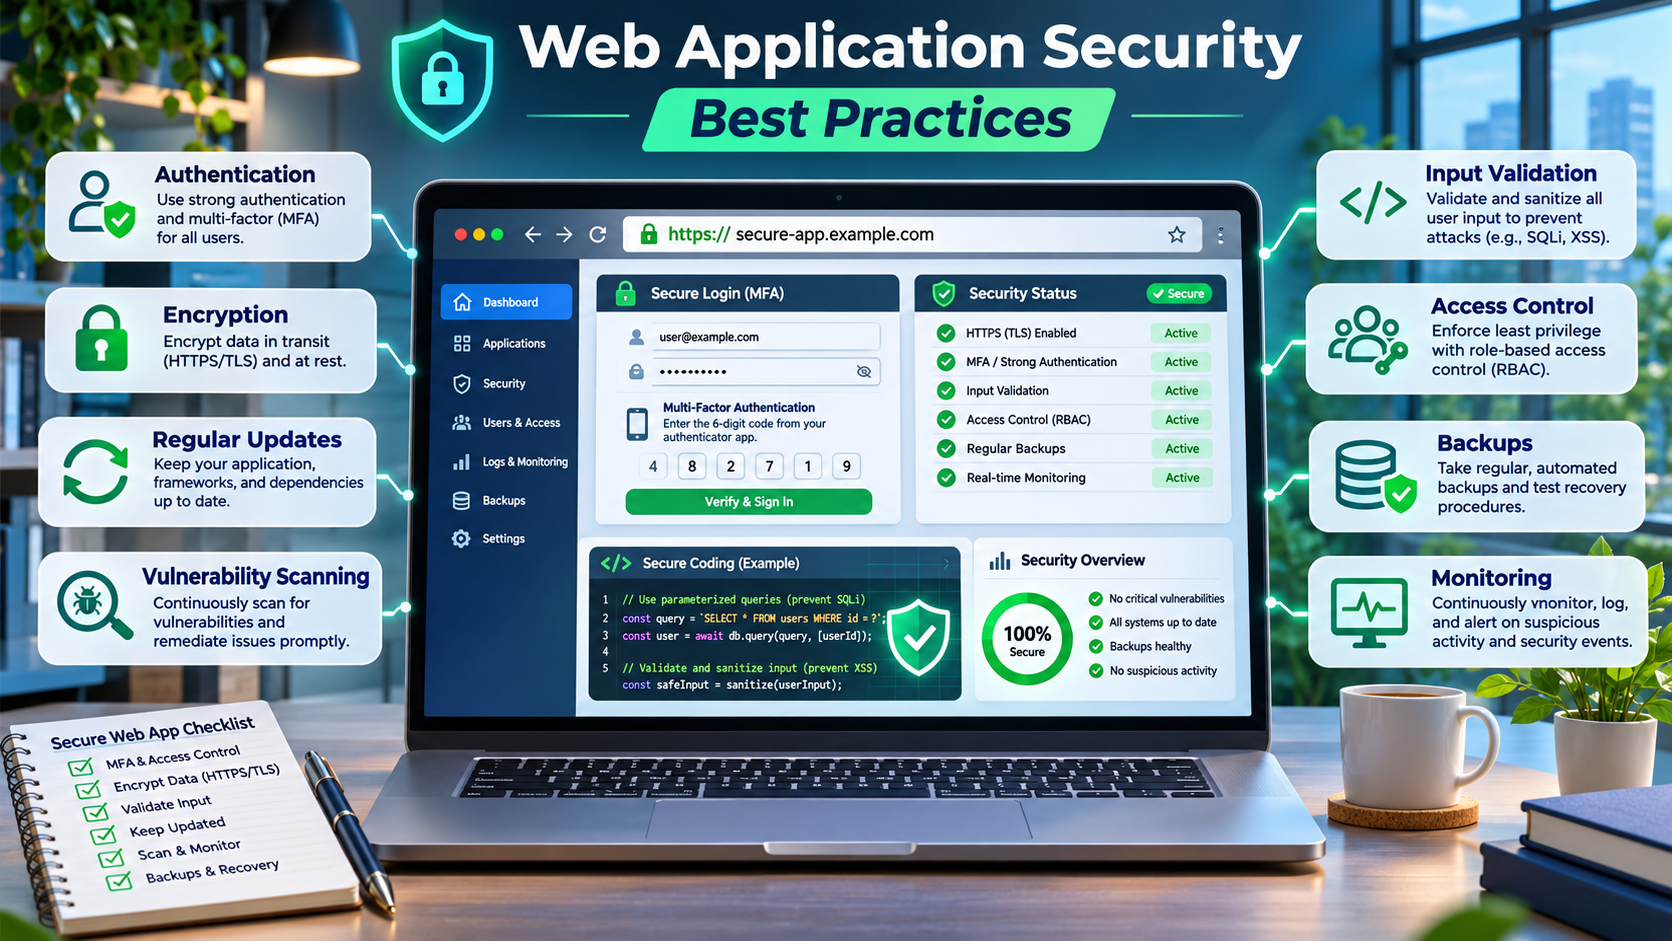
 A web application fails securely in layers, and it's worth separating two things that get talked about as one: how your server and hosting environment are configured, and how the application itself — its code, its logic, the data it handles — is built. A hardened server cannot fix a SQL injection flaw in your own code, and secure code running on an unpatched, unmonitored server is still exposed. This guide focuses on the application layer — the practices a developer, site owner, or technical lead can act on directly — and points to dedicated guides on this site for the server and certificate side of the picture rather than repeating them.
None of this amounts to a guarantee. No set of practices makes a web application immune to every attack, and anyone promising that is overselling. What a disciplined set of practices does is close the common, well-understood paths attackers actually use, which removes the overwhelming majority of real-world risk at a reasonable cost.
Start From a Recognized Framework
Rather than building a security checklist from scratch, most teams are better served starting from OWASP, a nonprofit foundation that maintains the most widely referenced web application security resources. The OWASP Top 10 names the categories of risk responsible for the large majority of real-world web application breaches — things like broken access control, cryptographic failures, injection flaws, security misconfiguration, and vulnerable or outdated components — and it's revised periodically as the threat landscape shifts, so it's worth checking you're looking at the current edition rather than one a few years old.
For teams that want something more granular than a top-10 list, the OWASP Application Security Verification Standard (ASVS) breaks those categories down into specific, checkable requirements at different levels of rigor, which makes it useful as an actual audit checklist rather than just a reading list.
Our own Cybersecurity: 15 Types of Web Attacks to Watch Out For covers how these attacks actually work in detail — SQL injection, cross-site scripting, CSRF, session hijacking and the rest — so this guide won't re-explain the mechanics. What follows is organized the other way around: by the defensive practice, not the attack name.
Authentication and Session Management
Set a sane password policy. Current guidance from NIST's Digital Identity Guidelines (SP 800-63B) favours length over complexity: a longer passphrase that a person can actually remember beats a short password forced through arbitrary character-class rules, and forced periodic rotation without cause tends to push people toward weaker, more predictable patterns rather than stronger ones. Screening new passwords against a list of known-breached credentials does more for real security than another complexity rule.
Add multi-factor authentication, at minimum for administrative accounts, and ideally for all accounts that can take a sensitive action. MFA is one of the single highest-value controls available, because it remains effective even after a password has leaked. Our two-factor authentication plugins for WordPress covers tactical options if that's your platform.
Store passwords with a modern, slow hashing algorithm — Argon2id where available, or bcrypt — with a unique salt per user. Fast general-purpose hashes like unsalted MD5 or SHA-1 were never appropriate for passwords and remain a common finding in security reviews of older applications.
Handle sessions deliberately: generate high-entropy, unpredictable session identifiers; mark session cookies Secure, HttpOnly and SameSite so they aren't sent over plain HTTP, aren't reachable from JavaScript, and aren't attached to unrelated cross-site requests; invalidate the session server-side on logout rather than relying on the client to discard it; and apply both an idle timeout and an absolute maximum session lifetime.
Rate-limit authentication endpoints and lock out or progressively delay repeated failed attempts, to blunt brute-force and credential-stuffing attempts against login forms and password-reset flows.
Validate Every Input, Encode Every Output
Validate on the server, always. Client-side validation is a usability feature, not a security control — it's trivially bypassed by anyone who sends a request directly rather than through your form. Every input has to be checked again once it reaches the server, regardless of what the browser already did.
Prefer allow-lists to deny-lists. A rule that says what's permitted (this field accepts only digits; this field accepts only values from a fixed set) is far more reliable than a rule that tries to list everything dangerous, because the dangerous list is never actually complete.
Use parameterized queries or prepared statements for every database call that includes user-supplied data, rather than building SQL strings by concatenation. This single practice closes the large majority of SQL injection risk by construction, because it keeps user input from ever being interpreted as part of the query's structure.
Encode output for the context it lands in. Text inserted into an HTML page, a JavaScript variable, a URL, or an HTML attribute each need different encoding, and the most common cross-site scripting bugs come from encoding correctly for one context while the data actually lands in another. Most modern templating engines handle this automatically if you use them as intended and don't bypass their escaping to insert raw markup.
Handle file uploads with particular care: verify the actual file content rather than trusting the extension or declared MIME type, store uploaded files outside the web root or in a location with no script-execution permission, rename files on upload rather than preserving the submitted filename, and scan uploads where the risk warrants it.
Enforce Access Control on Every Request
Check authorization server-side, on every request that touches protected data or functionality — not only by hiding a button or menu item in the interface. A hidden link is not a control; anyone who guesses or replays the underlying request still reaches it if the server doesn't check.
Verify object-level ownership, not just login status. The common failure here — often called an insecure direct object reference — is checking that a user is authenticated, then trusting an ID in the request (an invoice number, an account ID) without confirming that specific user is actually allowed to access that specific record. Changing one digit in a URL shouldn't open someone else's data.
Default to deny. New routes, new API endpoints and new admin functions should require an explicit access rule before they're reachable, rather than being open by default until someone remembers to lock them down.
Apply least privilege throughout the stack: a database account used by the application should hold only the permissions the application actually needs (a reporting connection has no business holding DROP TABLE rights), and file and directory permissions on the server should follow the same principle.
Protect Data in Transit and at Rest
Every page that handles a login, a form, or any personal or payment information should be served over HTTPS, with HTTP requests redirected in a single hop rather than a chain. Choosing and correctly configuring an SSL certificate — validation level, coverage, renewal automation, and TLS version settings on the server — is its own decision with real nuance, and it's one we cover in full in our guide to choosing the right SSL certificate rather than repeating here. The short version: a domain-validated certificate from a publicly trusted authority, renewed automatically, on a server configured for TLS 1.3 and 1.2 only, covers the large majority of sites well.
Encrypt sensitive data at rest, not only in transit — database-level or column-level encryption for anything genuinely sensitive, and backups that are encrypted as well as the live system, since a backup is a copy of the same sensitive data sitting somewhere else.
Keep sensitive values out of logs. Full card numbers, passwords, session tokens, and full request bodies on authentication endpoints have no business in a plaintext application log; mask or omit them at the point the log entry is written, not after the fact.
Harden the Server and Hosting Environment Underneath the Application
None of the application-layer practices above do much good on a server that's misconfigured or left unpatched, so the hosting layer deserves deliberate attention rather than an assumption that it's "someone else's job." A well-run Linux hosting plan gives you a meaningfully easier starting point here than configuring everything yourself on a bare server: sane default file permissions, isolated accounts, a managed PHP or runtime version you can update without rebuilding the server by hand, and automated backups as a baseline rather than an afterthought.
- Turn off directory listing, and remove or disable services and modules you don't actually use.
- Make sure error pages shown to visitors don't leak stack traces, file paths, or software version numbers — that information is free reconnaissance for an attacker.
- Set security headers at the server or application level: a Content Security Policy to restrict which script sources can execute, X-Frame-Options or a frame-ancestors directive against clickjacking, X-Content-Type-Options to stop MIME-type sniffing, and a sensible Referrer-Policy. Our 15 types of web attacks guide covers what each of these specifically defends against.
- Patch promptly and on a schedule, not only when something breaks. Website Patch Management covers how to set that cadence up and what's actually your responsibility versus your host's.
If security is a stated priority when evaluating web hosting in Canada, judge a provider on concrete, checkable criteria rather than a marketing claim: automated backups and how often restores are actually tested, whether malware scanning or a web application firewall is included at the edge, how quickly server-side components get patched, and whether your site is isolated from other customers' sites or shares resources on a crowded plan. A Canadian data-centre location is a genuine, measurable latency benefit for a Canadian audience and a simpler story for where customer data physically sits — it isn't, on its own, evidence of better application security, which is a separate question worth asking about directly.
Manage Dependencies and Supply-Chain Risk
A large share of real-world breaches trace back not to a flaw the development team wrote, but to a known, already-patched vulnerability in a plugin, library, framework, or CMS component nobody updated. Keep an inventory of what your application actually depends on, apply security updates for those components promptly, remove plugins and libraries you no longer use (an inactive plugin is still a live attack surface if it's still installed), and pull packages only from trusted registries rather than unofficial mirrors. For teams running continuous integration, a dependency-scanning step that flags known vulnerable versions before deployment catches this class of problem automatically rather than relying on someone remembering to check.
Log, Monitor, and Plan for the Incident You Hope Not to Have
Log the events that matter for security — failed logins, access-control failures, input-validation rejections, administrative actions — without logging the sensitive data involved in them. A log that records every failed login attempt is useful; a log that also records the password someone mistyped is a liability sitting right next to the problem it's meant to help you catch.
Decide your incident response steps before you need them, not while an incident is active: who gets notified, how sessions get revoked and credentials rotated, how a clean backup gets restored, and what you're obligated to disclose and to whom. Figuring that out for the first time during an actual breach costs real time, and time is the one resource an active incident doesn't give you.
Keep backups that are both regular and tested. A backup nobody has ever restored from is a hope, not a plan — schedule an actual test restore periodically so the first time you find out a backup doesn't work isn't the day you need it.
Test Before You Ship, Not After Something Breaks
- Run static analysis (SAST) and dependency scanning as part of your build or deployment pipeline, so a known vulnerable pattern or package version is flagged before it reaches production, not discovered after.
- Keep a staging environment that's genuinely separate from production — separate database, separate credentials, and (per our SSL certificate guide) its own certificate rather than one shared with the live site — so testing never risks real customer data.
- Schedule periodic vulnerability scanning or penetration testing proportional to what the application actually handles; a site processing payments or health information warrants more scrutiny than a brochure site, and the right cadence follows from that, not from a fixed rule.
Where Hosting Security Ends and Application Security Begins
It's worth being precise about the boundary, because vendors on both sides of it sometimes blur it. Your hosting provider's job — patch the server OS and control panel, filter malicious traffic at the edge, keep the physical and network infrastructure available and isolated — is necessary and valuable, and it's the subject of why the website itself is now the security perimeter and of how shared responsibility actually works between a cloud or hosting provider and its customers. But none of that writes parameterized queries, encodes your output correctly, or checks that a user is actually authorized to see record 4,502. That part is the application's own job, and it's what this guide has focused on.
A Practical Web Application Security Checklist
- Map your practices against the current OWASP Top 10 and treat gaps as a prioritized backlog, not a one-time audit.
- Enforce a sane password policy (length over complexity) and require MFA at least for administrative accounts.
- Hash passwords with Argon2id or bcrypt and a unique per-user salt; never a fast general-purpose hash.
- Set Secure, HttpOnly and SameSite on session cookies; invalidate sessions server-side on logout.
- Validate every input server-side with allow-lists; never rely on client-side validation alone.
- Use parameterized queries for every database call that includes user input.
- Encode output correctly for its context (HTML, JavaScript, URL, attribute).
- Validate uploaded files by content, store them outside the web root, and rename them on upload.
- Check authorization server-side on every request, including object-level ownership, not just login status.
- Apply least privilege to database accounts and file permissions throughout the stack.
- Serve every sensitive page over HTTPS with a correctly configured, auto-renewing SSL certificate.
- Encrypt sensitive data and backups at rest, and keep sensitive values out of plaintext logs.
- Set core security headers (CSP, frame-ancestors, X-Content-Type-Options, Referrer-Policy).
- Patch the application, its dependencies, and the server on a schedule, not only when something breaks.
- Remove unused plugins and libraries rather than leaving them installed and dormant.
- Log security-relevant events without logging the sensitive data inside them.
- Write an incident response plan before you need one, and test your backup restores on a schedule.
- Run static analysis and dependency scanning in your build pipeline, and keep staging genuinely separate from production.
FAQ
What's the difference between web application security and hosting security?
Hosting security covers the server, network, and infrastructure layer — patching the operating system, filtering traffic at the edge, keeping hardware and backups available. Web application security covers the code and logic layer — how input is validated, how access control is enforced, how sessions and passwords are handled. Both matter, and neither substitutes for the other: a hardened server doesn't fix a SQL injection flaw in your own code.
What is the OWASP Top 10?
It's a periodically revised list, maintained by the OWASP Foundation, of the categories of risk responsible for most real-world web application breaches — things like broken access control, cryptographic failures, injection flaws, and security misconfiguration. It's widely used as a baseline checklist precisely because it's framework-neutral and revised as the threat landscape changes.
Is an SSL certificate enough to secure a web application?
No. A certificate encrypts data in transit and confirms the server is authorized for the domain — it does nothing for a SQL injection flaw, a weak password policy, or a vulnerable plugin. It's one necessary layer among several, not a substitute for the others.
How should passwords be stored?
With a slow, modern hashing algorithm designed for passwords — Argon2id or bcrypt — and a unique salt per user, never a fast general-purpose hash like unsalted MD5 or SHA-1. Current guidance also favours a long passphrase over forced character-class complexity and arbitrary rotation rules.
What is the single highest-value security control for most small sites?
There's no universal single answer, but multi-factor authentication on administrative accounts and parameterized queries for every database call are both unusually high-value relative to their implementation cost, because they close two of the most commonly exploited paths by construction rather than by hoping every edge case was caught.
Does my hosting provider handle web application security for me?
Partially. A good host patches the server, isolates your account, and may offer a web application firewall or malware scanning at the edge — but application-level practices like input validation, access control checks, and session handling live in your own code or platform configuration, and no hosting plan writes those for you.
How often should dependencies and plugins be updated?
On a regular schedule, not only when something visibly breaks — most real-world breaches that trace back to a component exploit a vulnerability that already had a published patch. Removing unused plugins and libraries matters just as much, since an inactive one is still a live attack surface.
KEY TAKEAWAYS
- Web application security and hosting/server security are different layers; both matter, and neither substitutes for the other.
- OWASP's Top 10 and ASVS are the standard starting framework — check you're referencing the current edition.
- Authentication: favour long passphrases over forced complexity, require MFA on administrative accounts, and hash passwords with Argon2id or bcrypt.
- Validate every input server-side with allow-lists; use parameterized queries for database calls; encode output for its actual context.
- Enforce access control, including object-level ownership checks, on the server for every request — not only in the interface.
- An SSL certificate protects data in transit; it does nothing for application-layer flaws like injection or weak access control.
- Keep sensitive data encrypted at rest and out of plaintext logs.
- Patch dependencies and the server on a schedule; remove unused plugins and libraries rather than leaving them installed.
- Write an incident response plan and test backup restores before you ever need them.
- No set of practices guarantees immunity; the goal is closing the common, well-understood paths attackers actually use.
CONCLUSION
Web application security isn't one setting to turn on or one product to buy — it's a set of practices at every layer a request passes through: how a user proves who they are, how their input is checked, how access to data is confirmed, how that data is protected in transit and at rest, and how the server underneath all of it is configured and kept patched. Most real-world breaches don't come from a novel, unstoppable technique; they come from one of a well-documented, relatively short list of gaps — a missing server-side check, a password stored the wrong way, a dependency nobody updated. Working through the checklist above in order, and treating it as a standing practice rather than a one-time project, closes the large majority of that risk at a reasonable, sustainable cost.
READY TO START?
Put your idea online with Canadian web hosting
Hosting from Canadian data centres, cPanel included, and a real team you can call.
See hosting plans | or call 1-866-708-4678










